As FDPPI completes eight years of its existence, it is appropriate to look back not only at what the organization has accomplished, but also at why FDPPI was created in the first place.
Organizations often evolve considerably from the time of their formation. Programmes change, technologies change, laws change and the needs of the professional community change. Yet, a well-founded organization should retain a set of principles that provide continuity to its journey.
The objectives with which FDPPI was established were deliberately broader than the creation of a training or certification organization. They sought to establish a professional community that could contribute to the development of a secure and responsible information society.
The overarching objective was:
“To build an empowered community of Knowledgeable, Efficient and Ethical Data Protection Professionals who contribute to the development of a Secure Information Society by lawful means without any profit motive.”
Two specific objectives supported this larger vision:
1. To enhance the intrinsic Value and Worth of the profession of Data Protection Professionals who are directly or indirectly engaged in the activity of generating, managing, preserving and protecting information without any profit motive.
2. To bring harmony in the pursuance of Civil Rights of individuals such as Privacy and Freedom of Expression along with the Right to Information and Right to Cyber Security without any profit motive.
Eight years later, these objectives deserve a closer examination because the developments in Data Protection, Cyber Security, Artificial Intelligence and Data Governance have demonstrated their continuing relevance.
1. Building an empowered professional community
The first part of the FDPPI vision is the creation of an “empowered community”.
Empowerment is different from simply increasing the number of professionals.
A professional may possess a certificate without necessarily possessing the ability to deal with a complex real-world situation. Data Protection professionals are increasingly required to understand law, technology, business processes, information security, risk management, auditing and organizational governance.
The FDPPI objective therefore uses three important words:
Knowledgeable
A Data Protection professional must understand the applicable law and regulations, but legal knowledge alone is insufficient.
The professional must understand how personal data is collected, processed, stored, transferred, secured, retained and deleted. Increasingly, the professional must also understand how artificial intelligence systems use data and how technology can affect individual rights.
Efficient
Knowledge must translate into implementation.
Organizations need professionals who can convert legal requirements into policies, processes, controls, contracts, technology requirements, audit mechanisms and measurable compliance.
The professional must therefore be capable of asking:
What does the law require, and how can the organization actually implement it?
Ethical
Data Protection involves enormous power over information relating to individuals.
A professional dealing with personal data can influence how information is collected, used, disclosed and retained. Professional competence without ethical responsibility can therefore create its own risks.
FDPPI’s emphasis on ethical professionals recognizes that Data Protection is ultimately about trust.
2. Enhancing the value of the Data Protection profession
The first specific objective speaks about enhancing the “intrinsic Value and Worth” of the Data Protection profession.
This is important.
FDPPI was not created merely to help professionals obtain employment or commercial opportunities. Its objective was to establish Data Protection as a serious professional discipline.
The profession sits at the intersection of several disciplines:
- Law
- Cyber Security
- Information Technology
- Risk Management
- Governance
- Audit
- Compliance
- Business Management
- Artificial Intelligence
- Data Governance
The Data Protection professional therefore performs a role that cannot be reduced to checking whether a privacy policy exists.
A mature Data Protection professional should be able to understand the organization’s information ecosystem, identify risks, evaluate controls, advise management and participate in the creation of a trustworthy data environment.
This is why professional development is central to FDPPI.
3. Why the objective refers to people who generate, manage, preserve and protect information
Another interesting aspect of the original objective is that it does not restrict the professional community to people carrying the designation of DPO.
It refers to persons who are directly or indirectly involved in:
generating, managing, preserving and protecting information.
This is a much wider ecosystem.
A Data Protection programme can involve:
- Data Protection Officers
- Privacy professionals
- Cyber Security professionals
- Internal auditors
- Data auditors
- Legal professionals
- IT professionals
- Records and information managers
- Risk professionals
- Compliance professionals
- Business process owners
- AI governance professionals
- Consultants and educators
This broad definition has enabled FDPPI to evolve beyond a conventional professional association.
It also explains the subsequent development of different FDPPI initiatives, including professional certification, DGPSI and AIDAI.
4. The objective of “harmony” between different rights
The second objective perhaps represents one of the most distinctive aspects of the FDPPI philosophy.
It speaks about bringing harmony between:
- Privacy
- Freedom of Expression
- Right to Information
- Right to Cyber Security
This formulation is important because rights relating to information do not always operate independently.
There can be legitimate situations in which one interest appears to conflict with another.
For example:
Privacy may require restricting disclosure of personal information.
At the same time, the Right to Information may support transparency in matters involving public interest.
Freedom of Expression may require the ability to communicate information or opinions.
At the same time, organizations and individuals have legitimate interests in protecting information from unauthorized access, manipulation or destruction.
Cyber Security protects the integrity and availability of information, but security controls should themselves operate within the framework of law and respect legitimate rights.
The FDPPI objective does not suggest that one of these interests should automatically prevail over the others.
Instead, it uses the word:
“Harmony”
Harmony requires a framework for understanding the legitimate interests involved and applying the law in a balanced manner.
This becomes particularly important in a digital society where information can be copied, distributed and processed at unprecedented speed.
5. From Privacy Protection to Data Governance
When FDPPI was conceived, Data Protection in India was still developing as a distinct professional discipline.
The Information Technology Act, 2000, including Section 43A, was an important part of the legal framework. Subsequently, the country went through several stages of proposed Data Protection legislation before arriving at the Digital Personal Data Protection Act.
During the same period, the technology landscape changed dramatically.
Cloud computing became mainstream.
Mobile applications became ubiquitous.
Artificial Intelligence emerged as a transformational technology.
Organizations began processing enormous volumes of personal and non-personal data.
Data became an important organizational asset.
Consequently, Data Protection could no longer be viewed only as a question of privacy notices and consent.
It became a question of Data Governance.
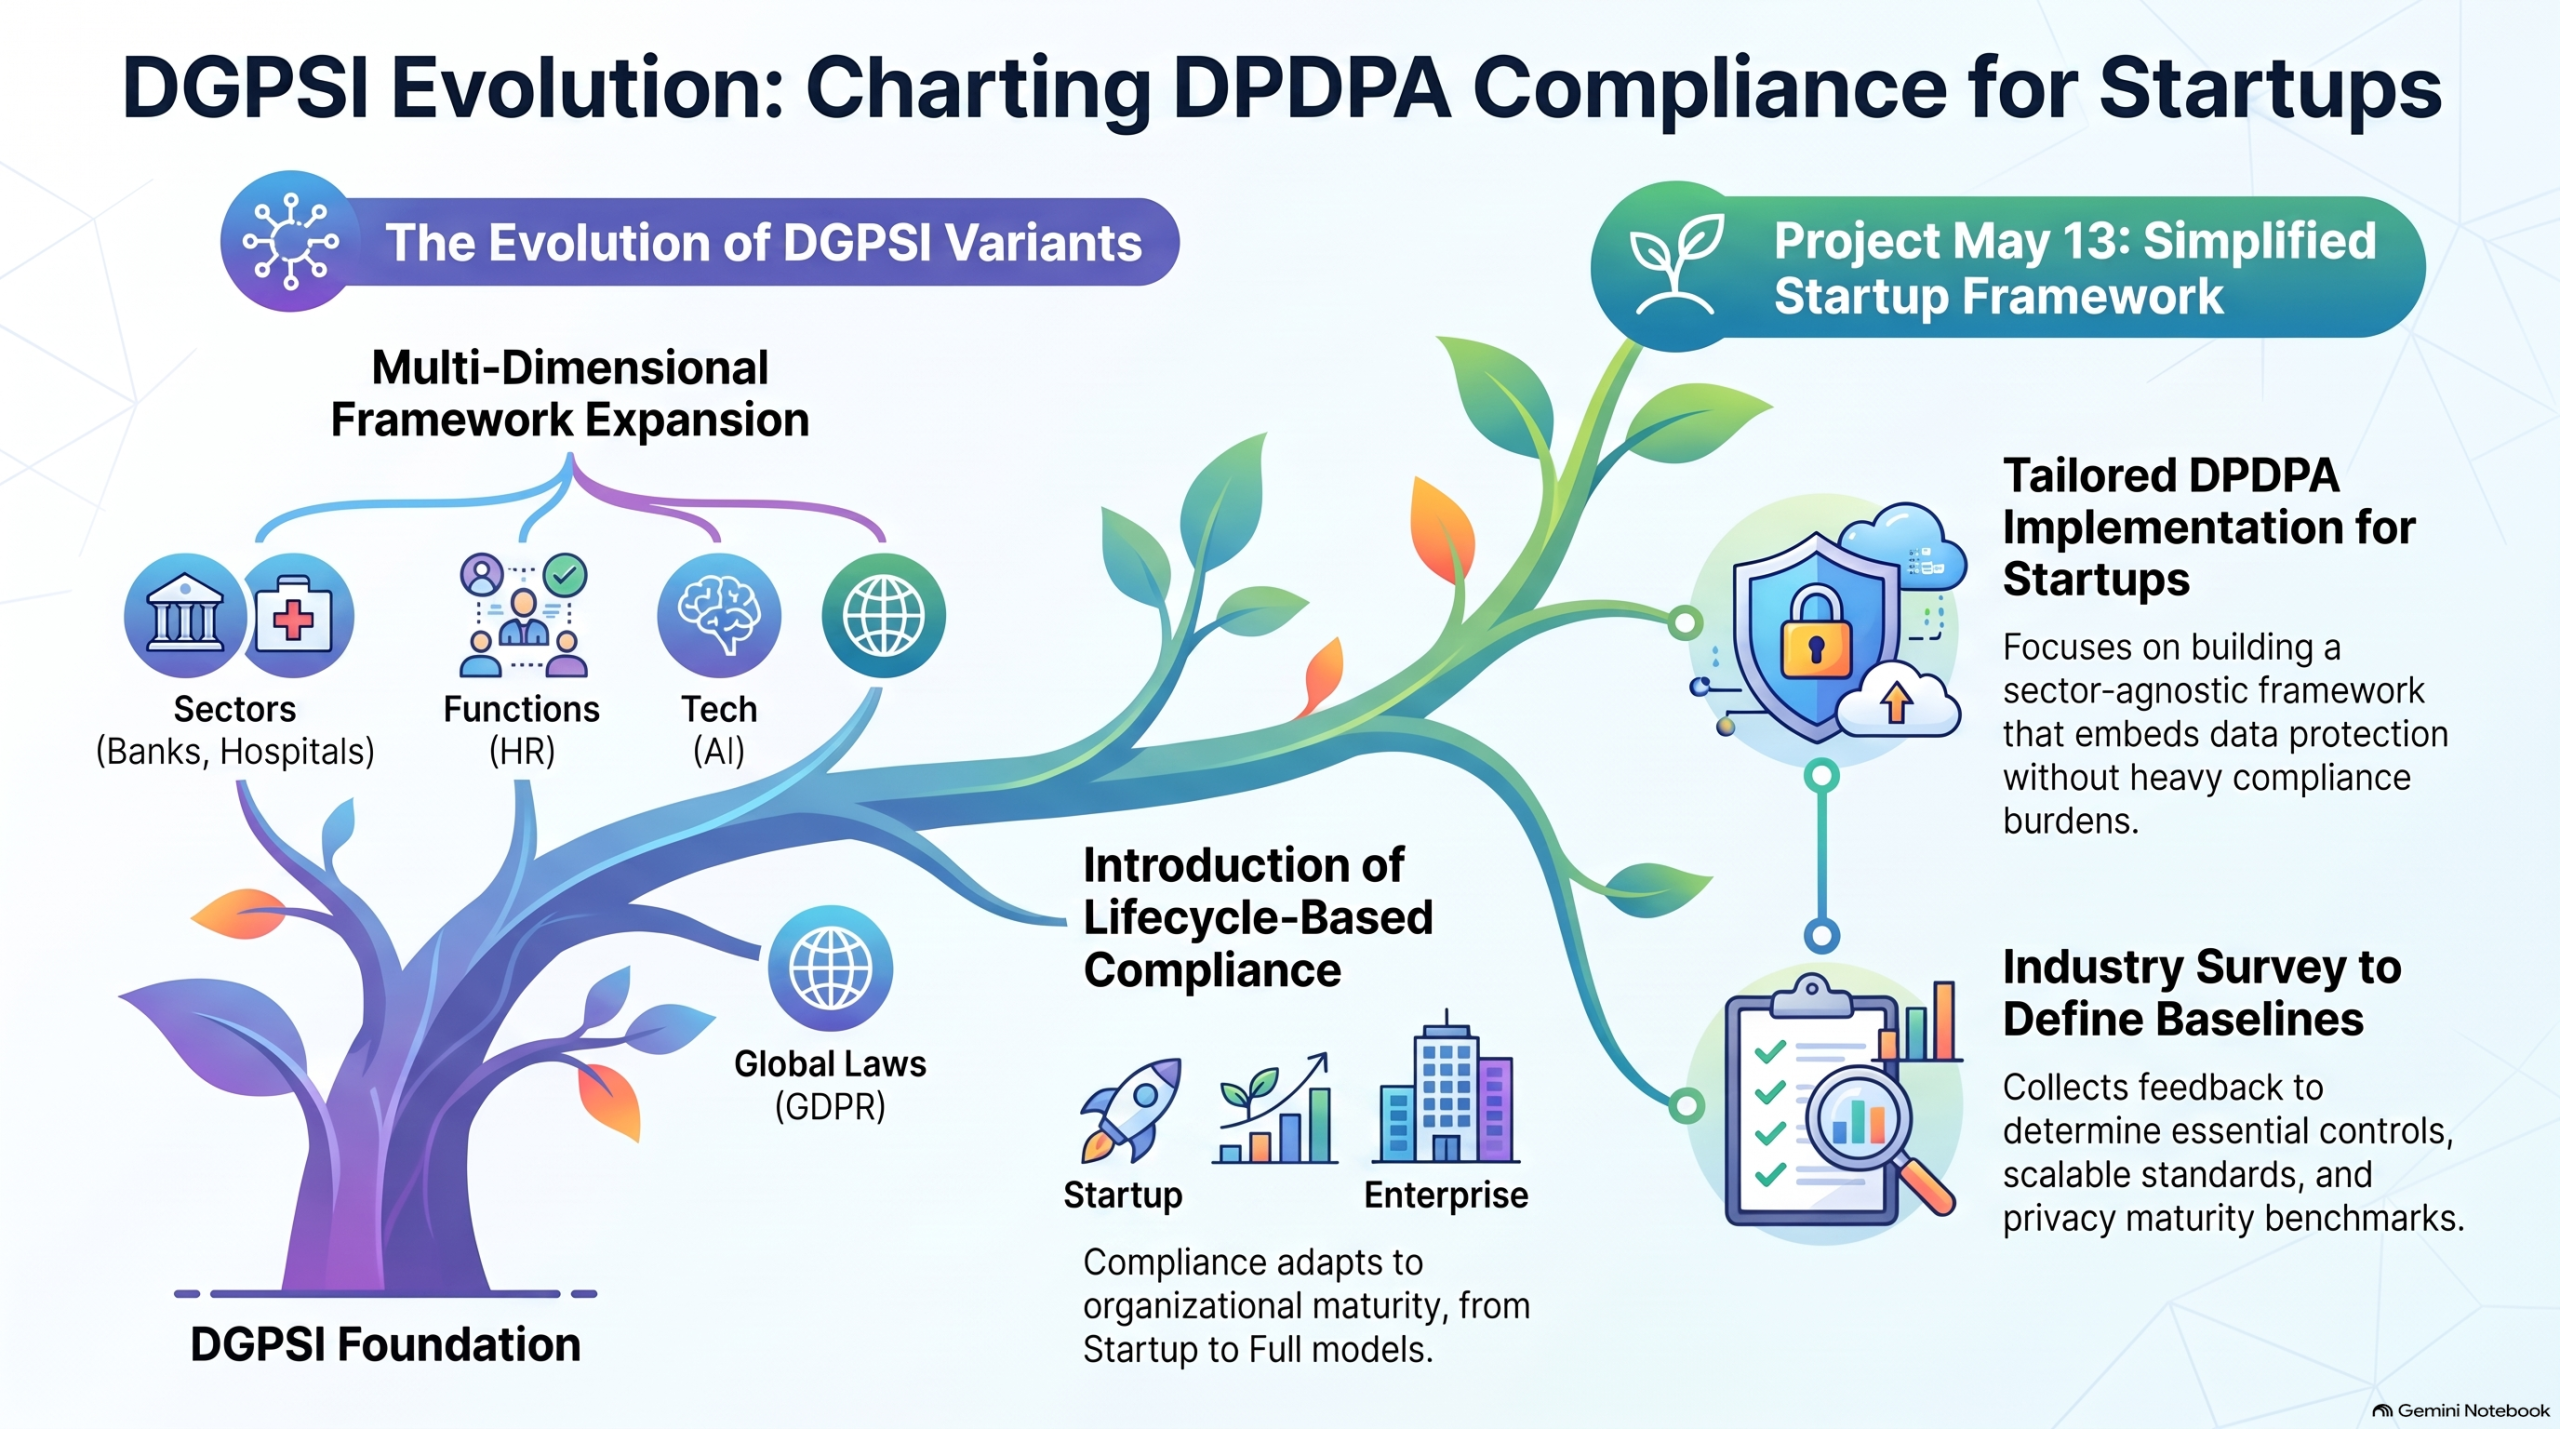
This evolution is reflected in FDPPI’s development of the DGPSI — Data Governance and Protection Standard of India.
6. From professional education to standards development
FDPPI’s journey can therefore be understood as an evolution through several stages.
Stage 1 — Awareness and Education
The first requirement was to create awareness about Data Protection and develop professional knowledge.
Stage 2 — Certification
The next requirement was to establish measurable professional competence through structured education and certification.
Stage 3 — Standards
As organizations began asking a more fundamental question — “How do we actually implement Data Protection?” — the need for implementation frameworks became evident.
This contributed to the development of DGPSI.
Stage 4 — Audit
As compliance frameworks mature, organizations need independent mechanisms to evaluate whether the claimed compliance actually exists.
This is the context in which AIDAI — Association of Independent Data Auditors of India assumes importance.
Thus, the journey has not been a series of unrelated initiatives.
It represents an evolution:
Education → Certification → Standards → Implementation → Audit
7. The significance of “without any profit motive”
The phrase “without any profit motive” appears in the objectives and deserves clarification.
It does not mean that Data Protection professionals should work without remuneration.
Professionals obviously need to be compensated for their knowledge, time and services.
The expression refers to the institutional purpose of FDPPI.
As a Section 8 organization, FDPPI exists for its stated objectives and not for distribution of profits to shareholders.
This distinction is important.
A professional organization can facilitate professional opportunities while itself remaining committed to a larger public-interest objective.
The ultimate beneficiary is therefore not merely the member.
It is the information society.
8. The objectives and the DPDPA era
India is now entering a fundamentally different phase.
The Digital Personal Data Protection framework is creating new responsibilities for organizations and new professional requirements.
Data Fiduciaries will need to understand their obligations.
Data Principals will need mechanisms through which their rights can be exercised.
Data Processors will need appropriate contractual and operational arrangements.
Significant Data Fiduciaries will have additional governance requirements.
Organizations will need policies, processes, technical controls, documentation, risk management and audit mechanisms.
This creates a requirement for professionals who are not merely familiar with the terminology of Data Protection but who can translate law into operational governance.
That requirement is precisely aligned with the original FDPPI objective of creating professionals who are knowledgeable, efficient and ethical.
9. The future: Data Protection, AI and independent audit
The next phase of FDPPI’s journey is likely to be shaped by three interconnected developments:
Data Protection
The implementation of India’s Data Protection framework will create a substantial requirement for professional knowledge and organizational capability.
Artificial Intelligence Governance
AI introduces questions that go beyond traditional privacy compliance.
Questions concerning data provenance, automated decision-making, algorithmic governance, accountability and responsible deployment require new governance approaches.
This is the background to FDPPI’s work on AIGSI — Artificial Intelligence Governance Standard of India.
Independent Data Audit
As organizations begin to demonstrate their compliance, independent assessment becomes increasingly important.
This is the rationale behind AIDAI and the development of frameworks for professional Data Auditing.
The objective is not to create another layer of bureaucracy.
It is to create confidence in the claims of compliance.
10. The Banyan Tree philosophy
The original objectives also provide a useful explanation for FDPPI’s organizational philosophy.
FDPPI does not necessarily aspire to become a large centralized employer.
Instead, it seeks to build a professional ecosystem.
The Banyan Tree Model captures this philosophy.
A banyan tree begins with a central trunk but continuously develops branches. Some branches eventually take root and become supporting structures themselves.
Similarly, FDPPI’s members and Associate Members can develop their own professional capabilities, initiatives and services while contributing to the larger ecosystem.
The strength of the organization therefore does not depend solely upon the size of its central structure.
It depends upon the strength of the professional community around it.
11. Eight years later — the objectives remain the foundation
Looking back after eight years, FDPPI has moved through several stages:
From awareness to education.
From education to certification.
From certification to professional development.
From professional development to standards.
From standards to implementation frameworks.
From implementation to independent audit.
And now, increasingly:
From Data Protection to Data Governance and AI Governance.
The instruments have changed.
The technology has changed.
The law has changed.
The professional requirements have changed.
But the fundamental objectives remain remarkably relevant.
FDPPI continues to seek the development of a community of professionals who are:
Knowledgeable.
Efficient.
Ethical.
And committed to contributing to a Secure Information Society by lawful means.
At the same time, FDPPI continues to believe that Privacy should not exist in isolation from other legitimate rights and interests.
The objective is not to create conflict between Privacy, Freedom of Expression, Right to Information and Cyber Security.
The objective is to develop the knowledge, professional competence and governance mechanisms required to achieve harmony among them.
That philosophy was embedded in FDPPI at its birth.
Eight years of experience have only demonstrated its continuing relevance.
The next phase is not merely about creating more Data Protection professionals.
It is about creating a professional ecosystem capable of making India’s information society more secure, trustworthy and responsible.
FDPPI’s original objectives remain the foundation for that journey.