DPDPA is Here
Countdown to 13th May 2027
Google_site_search
Bing_site_search
-
Ask Vishy, the personal AI-assistant of Naavi for all your information on Naavi.org
-
-
-
Naavi
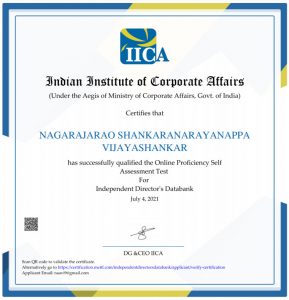
IICA Qualified Independent Director
-
-
DGPIN: 4PJ-7T8-FK8P: 12.94018310,77.55421020
-
Plus Code : WHR3+3P
-
Recent Posts
Archives
Archives by Date
-
-
Author Archives: Vijayashankar Na

AI Audit framework of CERT in compared with DPDPA centric Ai audit
The objective of AI Audit under DPDPA may be derived from a) Reasonable Security obligations under Rule number 6 b) Additional responsibilities of a Significant Data Fiduciary under Rule number 13 The concern of DPDPA related to AI is to … Continue reading
Posted in Privacy
Leave a comment
Towards a Unified AI Gudieline: CERT In Guideline 2 (AI Auditing)
….Continued CERT In which is a quasi judicial authority and the regulator under ITA 2000 is the nodal agency for Cyber Security in India. Under ITA 2000 it regulates organizations processing both personal data and non personal data under the … Continue reading
Posted in Privacy
Leave a comment
Towards Unified AIGSI: The DSCI Discussion Paper and the DGPSI-AI Approach
In Continuation of the earlier article on the emerging AI Guidelines Out of the nine AI-related guidelines identified in our earlier discussion, seven have already been examined on Naavi.org. We may revisit these documents at a later stage. For now, … Continue reading
Posted in Privacy
Leave a comment
The Nine AI guidelines..purpose identification
In yesterday’s post, we listed the following eight AI guidlines that have been released by different organizations in India. DGPSI-AI (Naavi/FDPPI): A DPDPA framework for Data Fiduciaries who carry AI risk either directly or through the processors. It mainly addressed … Continue reading
Posted in Privacy
Leave a comment